Malware Analysis — Part-2 Basic Dynamic Analysis
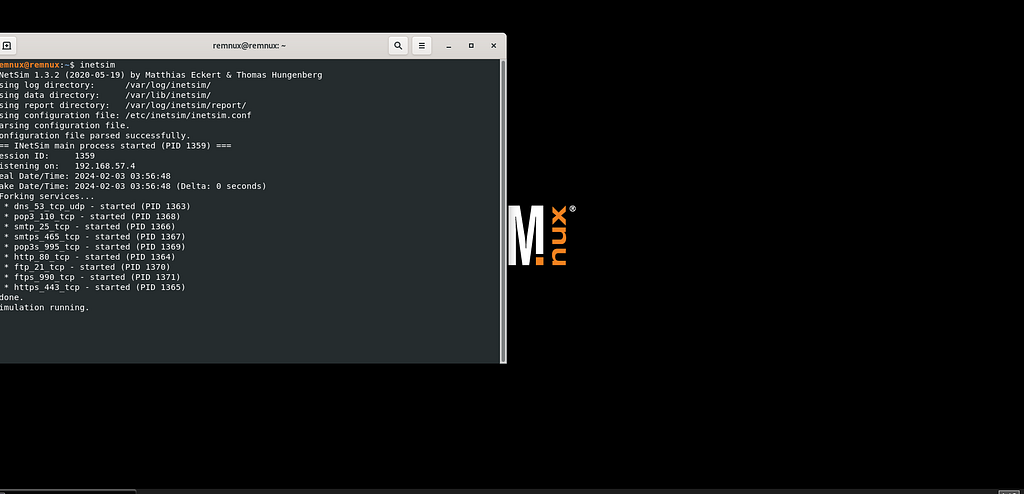
Run a malware sample in a controlled lab and trace its behavior with Wireshark, Procmon, and INetSim.
2 posts tagged “Malware Analysis”.
Run a malware sample in a controlled lab and trace its behavior with Wireshark, Procmon, and INetSim.
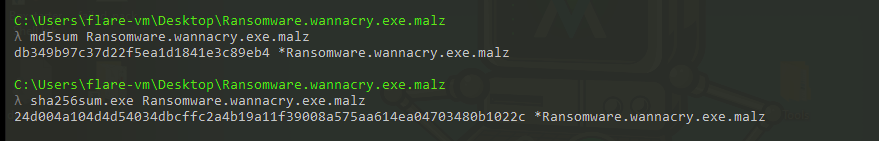
Inspect a suspicious binary without executing it using hashes, strings, FLOSS, PEview, and PEStudio.